


 57 Huynh Thuc Khang - Dong Da - Hanoi

 02435533388
 vnptit@vnpt.vn

 Contact
On the afternoon of 26/10/2026, VNPT Cyber Immunity (the VNPT Information Security Center under the VNPT Group) hosted Security Talk webinar 03 on the topic “Navigating compliance with cybersecurity and personal data protection decrees for businesses.” The webinar focused on analyzing real-world challenges and compliance implementation solutions, from legal and technical perspectives.
The year 2026 marks significant changes to the legal framework for cybersecurity and personal data protection. The question for businesses is no longer simply whether they need to comply, but how to comply correctly and fully, and provide evidence that they have done so.
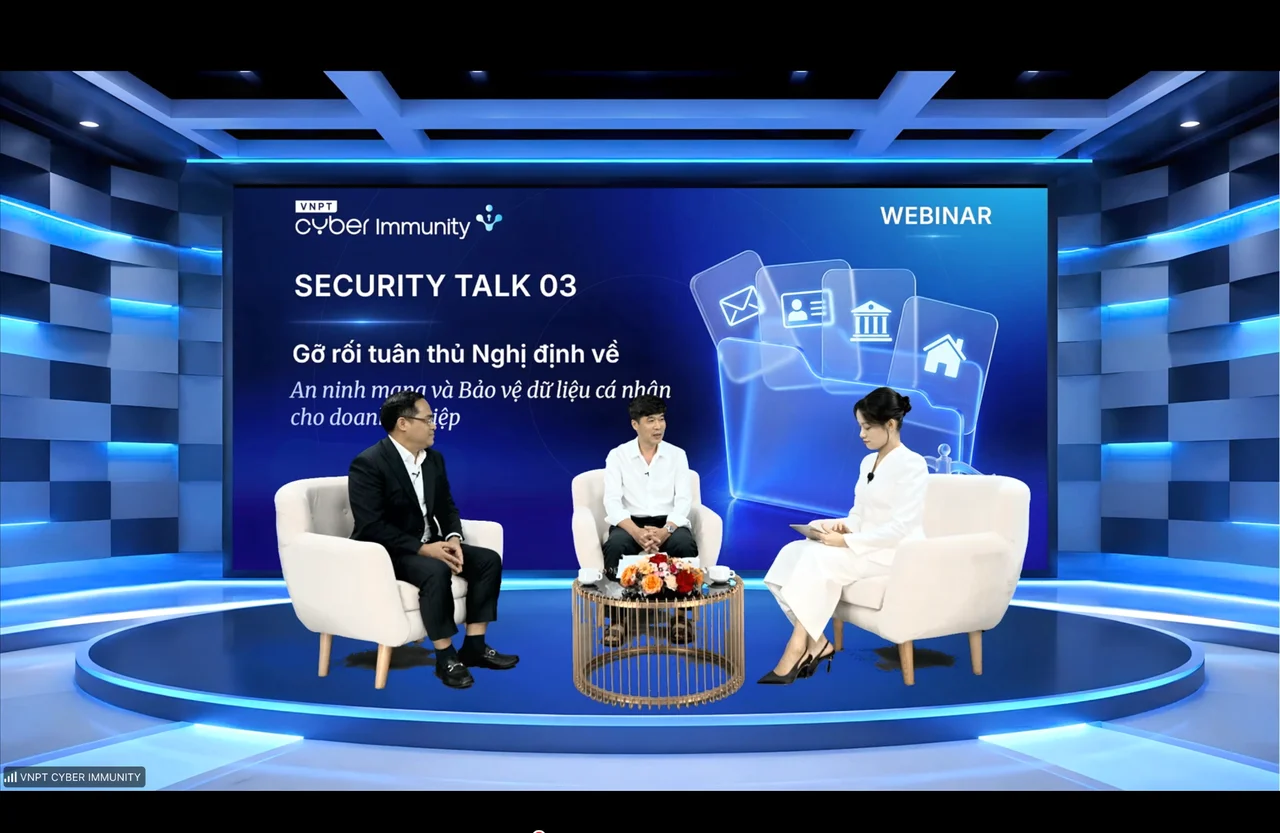
VCI Security Talk 03 on “Navigating compliance with the Decree on Cybersecurity and Personal Data Protection for Businesses”
Identifying obligations and legal risks correctly
At the webinar, Master of Laws and attorney Lưu Xuân Vĩnh, founding and managing attorney and head of the TMT & International Arbitration practice at Asia Legal, analyzed the key obligations businesses need to review, from the legal basis for processing personal data and obtaining data subjects’ consent to appointing responsible personnel, preparing impact assessment records, and safeguarding data subjects’ rights.
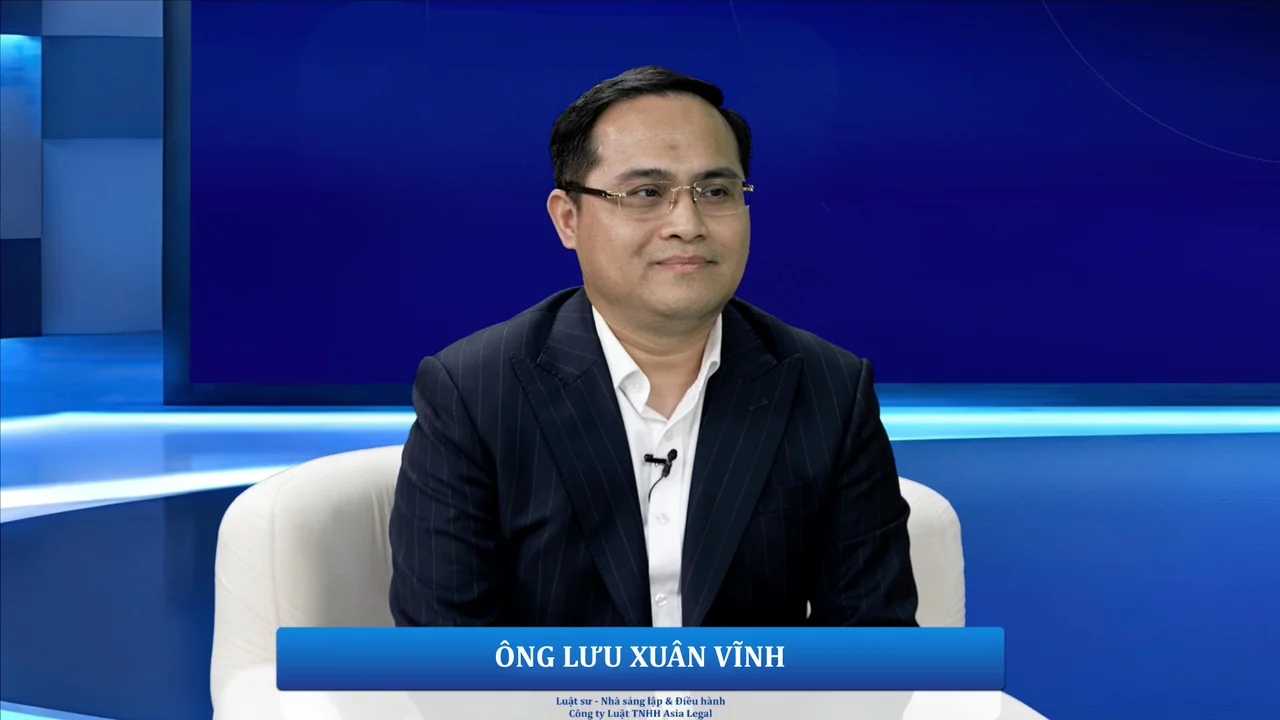
Lưu Xuân Vĩnh speaks at VCI Security Talk 03
In the area of cybersecurity, businesses need to determine the security level of their information systems, develop incident response plans, and assign responsibilities across departments. This is not solely the responsibility of legal or IT teams; it requires organization-wide coordination, with clear accountability from leadership.
Under Decree 330/2026/ND-CP, certain violations in the area of personal data protection may incur fines of up to billions of dong. Businesses should therefore identify risks early in activities such as recruitment, human resources management, marketing, and customer care. A common challenge is that businesses lack a data map and have not fully identified what data is collected, where it is stored or shared, and the responsibilities of each party. This is the basis for classifying data, determining obligations, and selecting appropriate compliance measures.
Outsourcing services does not mean transferring responsibility
For businesses using CRM software, cloud computing services, or providers with remote access, outsourcing does not automatically remove legal responsibility. The parties should clearly define their roles and the scope of data processing, and specify requirements for security, incident notification, data deletion, and audit rights in their contracts.
From a technical perspective, Đặng Quốc Bình, Process and Compliance Specialist at VNPT Cyber Immunity, discussed the challenges businesses face when operating legacy systems, using external services, or failing to fully control access rights. Measures such as access management, activity logging, encryption, and anomaly monitoring should be implemented in a way that suits the system’s characteristics and risk level.
Đặng Quốc Bình speaks at VCI Security Talk 03
Using a hypothetical scenario involving a ransomware attack that encrypts a human resources server, along with signs that data has been exfiltrated, the two guests discussed the initial incident response priorities: containing the impact, preserving digital evidence, coordinating across departments, and assessing regulatory notification obligations.
Businesses should also avoid waiting until an investigation is complete before considering notification, or transferring data to a parent company overseas without first assessing legal requirements. Preparing response procedures, contact points, and designated decision-makers in advance will help reduce risk.
Making compliance part of business as usual
For small and medium-sized businesses with limited resources, attorney Lưu Xuân Vĩnh recommends prioritizing three areas of work: mapping and classifying data; establishing foundational policies and procedures; and completing impact assessment records as required. Implementation should be based on risk levels and the nature of the business, rather than producing paperwork for appearances.
If a partner requests an inspection or assessment, businesses should prepare documents such as internal policies, evidence of consent, impact assessment records, data processing agreements, and incident logs. These records should be updated whenever systems or data processing activities change. Compliance is not just about understanding regulations or issuing documents; it must be implemented in practice and supported by corresponding evidence.
Through its Security Talk webinar series, VNPT Cyber Immunity (VCI), the cybersecurity brand of the VNPT Group, aims to support businesses in identifying risks, strengthening system and data protection, and proactively and sustainably integrating legal requirements into their operations.